


Access for everyone, managed in one place
Add people, assign roles, and control what they can connect, without needing a separate access layer for AI.
Without Upsun Dispatch
Access granted person by person
Each engineer connects their own tools with their own credentials. There's no single view of who has access to what.
No role distinction
An engineer, a security reviewer, and an admin all have the same level of access, or none at all.
Offboarding is a guess
When someone leaves, nobody's certain what they could still reach.
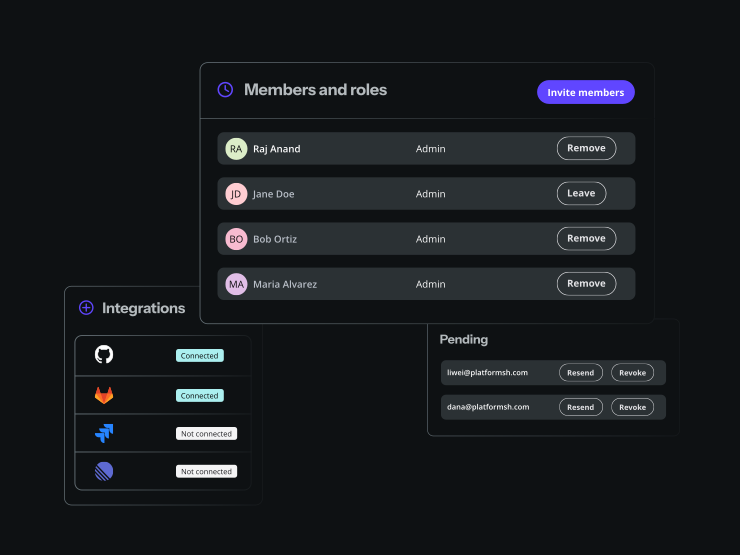
Defined roles. Access you can see.
Upsun Dispatch manages who's on your team, what role they hold, and what they're allowed to connect, in one place, visible to whoever administers it.
Built so access is never a guess
Every person on the team has a defined role, and every connection is visible to whoever manages the workspace.
- Role-based access across the whole workspace
- Repos and tools connected at the team level, not the individual's
- Admins can see every connection, not just their own
- Access revoked instantly when someone leaves
- Consistent across every project the team touches
How access gets managed
Add someone to the team
Invite a person and assign them a role: admin, engineer, reviewer, or a custom role you define.
Connect tools at the team level
Repos, issue trackers, and integrations are connected once, for the whole team, not per individual.
Roles determine reach
What a person can see or run follows from their role, not from whatever they happened to set up themselves.
Offboard in one step
Remove someone from the team, and every connection tied to their access goes with them.
Built for teams that need to know who can do what

Platform teams
See every person, role, and connection across the organization from one place.

Security teams
Confirm access follows least-privilege by design, not by individual habit.

Growing engineering orgs
Onboard new engineers with the right access from day one, without manual setup per person.

Regulated industries
Demonstrate exactly who had access to what, and when, for any audit.

Contractors and external staff
Grant scoped, temporary access without giving full team-level permissions.

Multi-team organizations
Keep roles and access consistent across every team, rather than reinvented per group.
Know who has access before it becomes a question.
Stay updated
Upsun Cloud: compliant and validated